Grant VeloDB Cloud Access to Your VPC
Software as a service (SaaS) warehouses only. Use this option when a VeloDB Cloud warehouse needs to access a private data source in your virtual private cloud (VPC) or virtual network (VNet), such as a database used for an import or integration job.
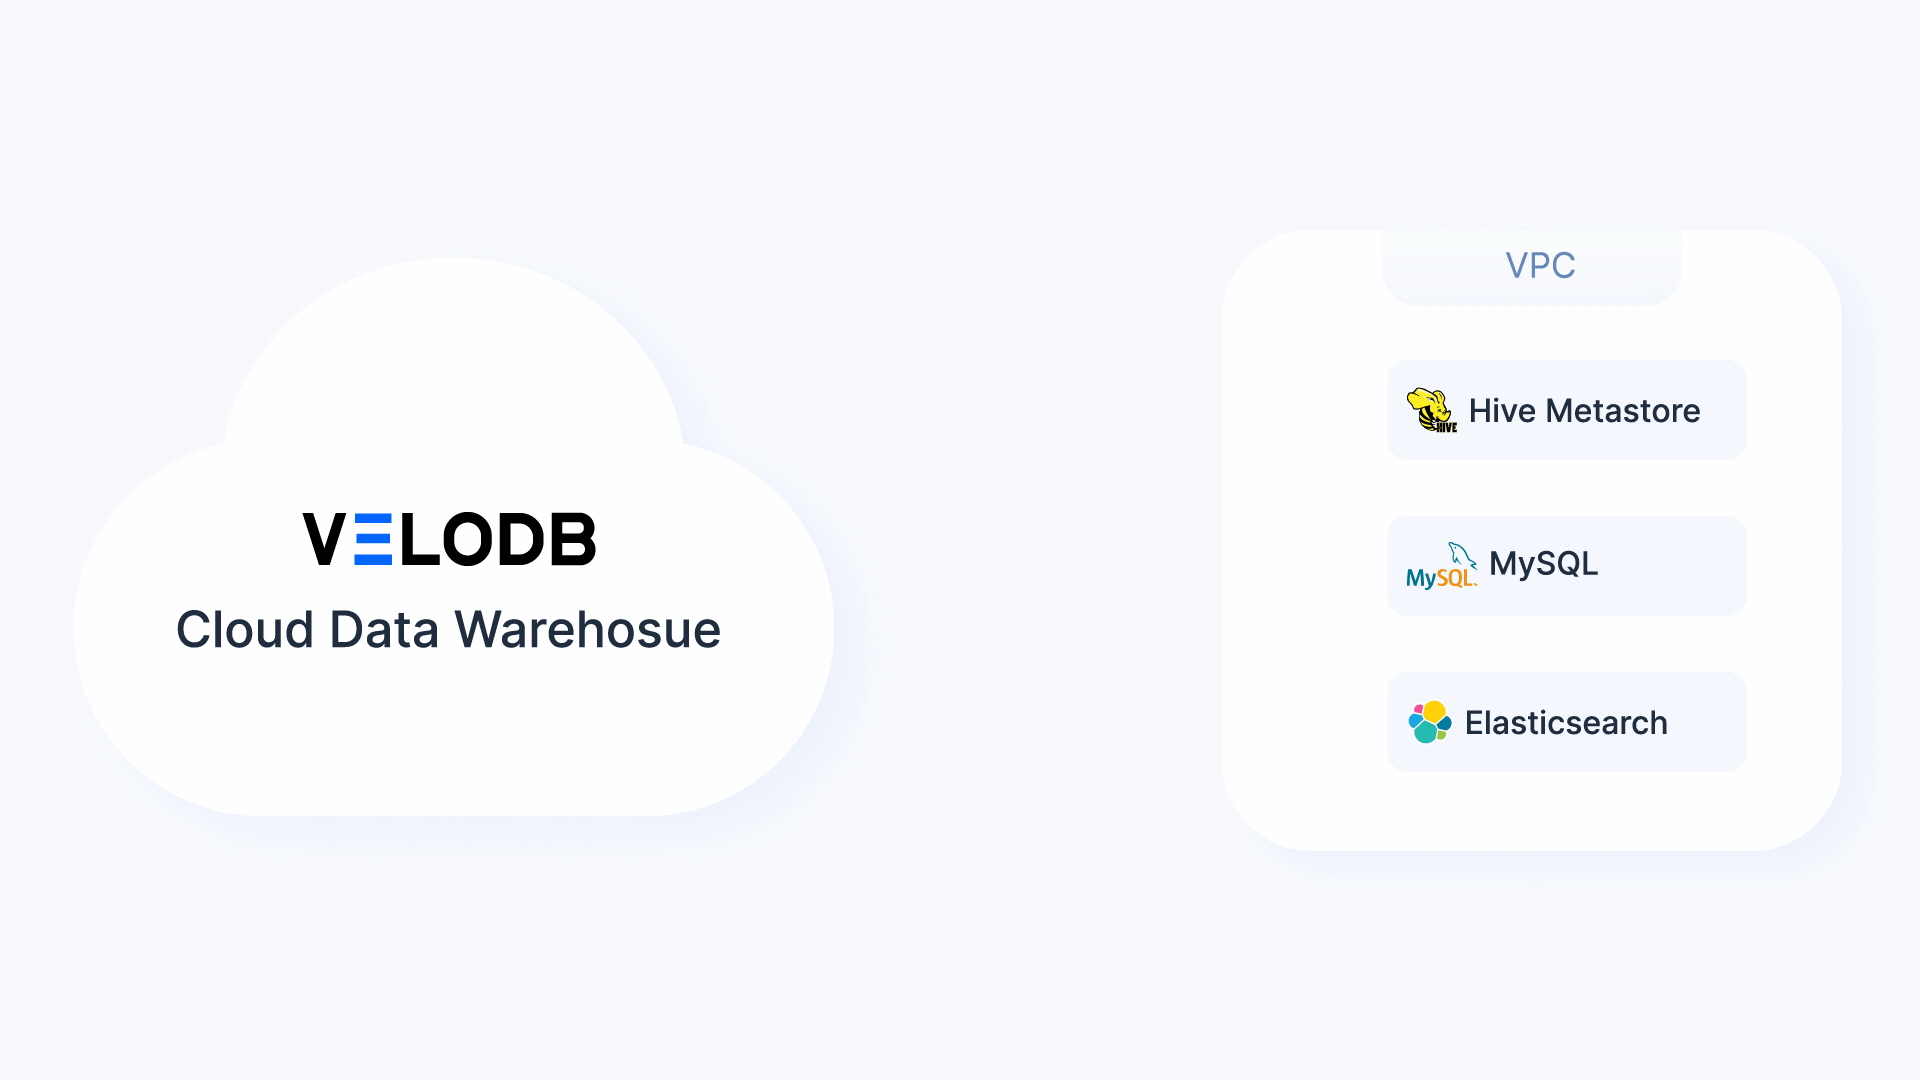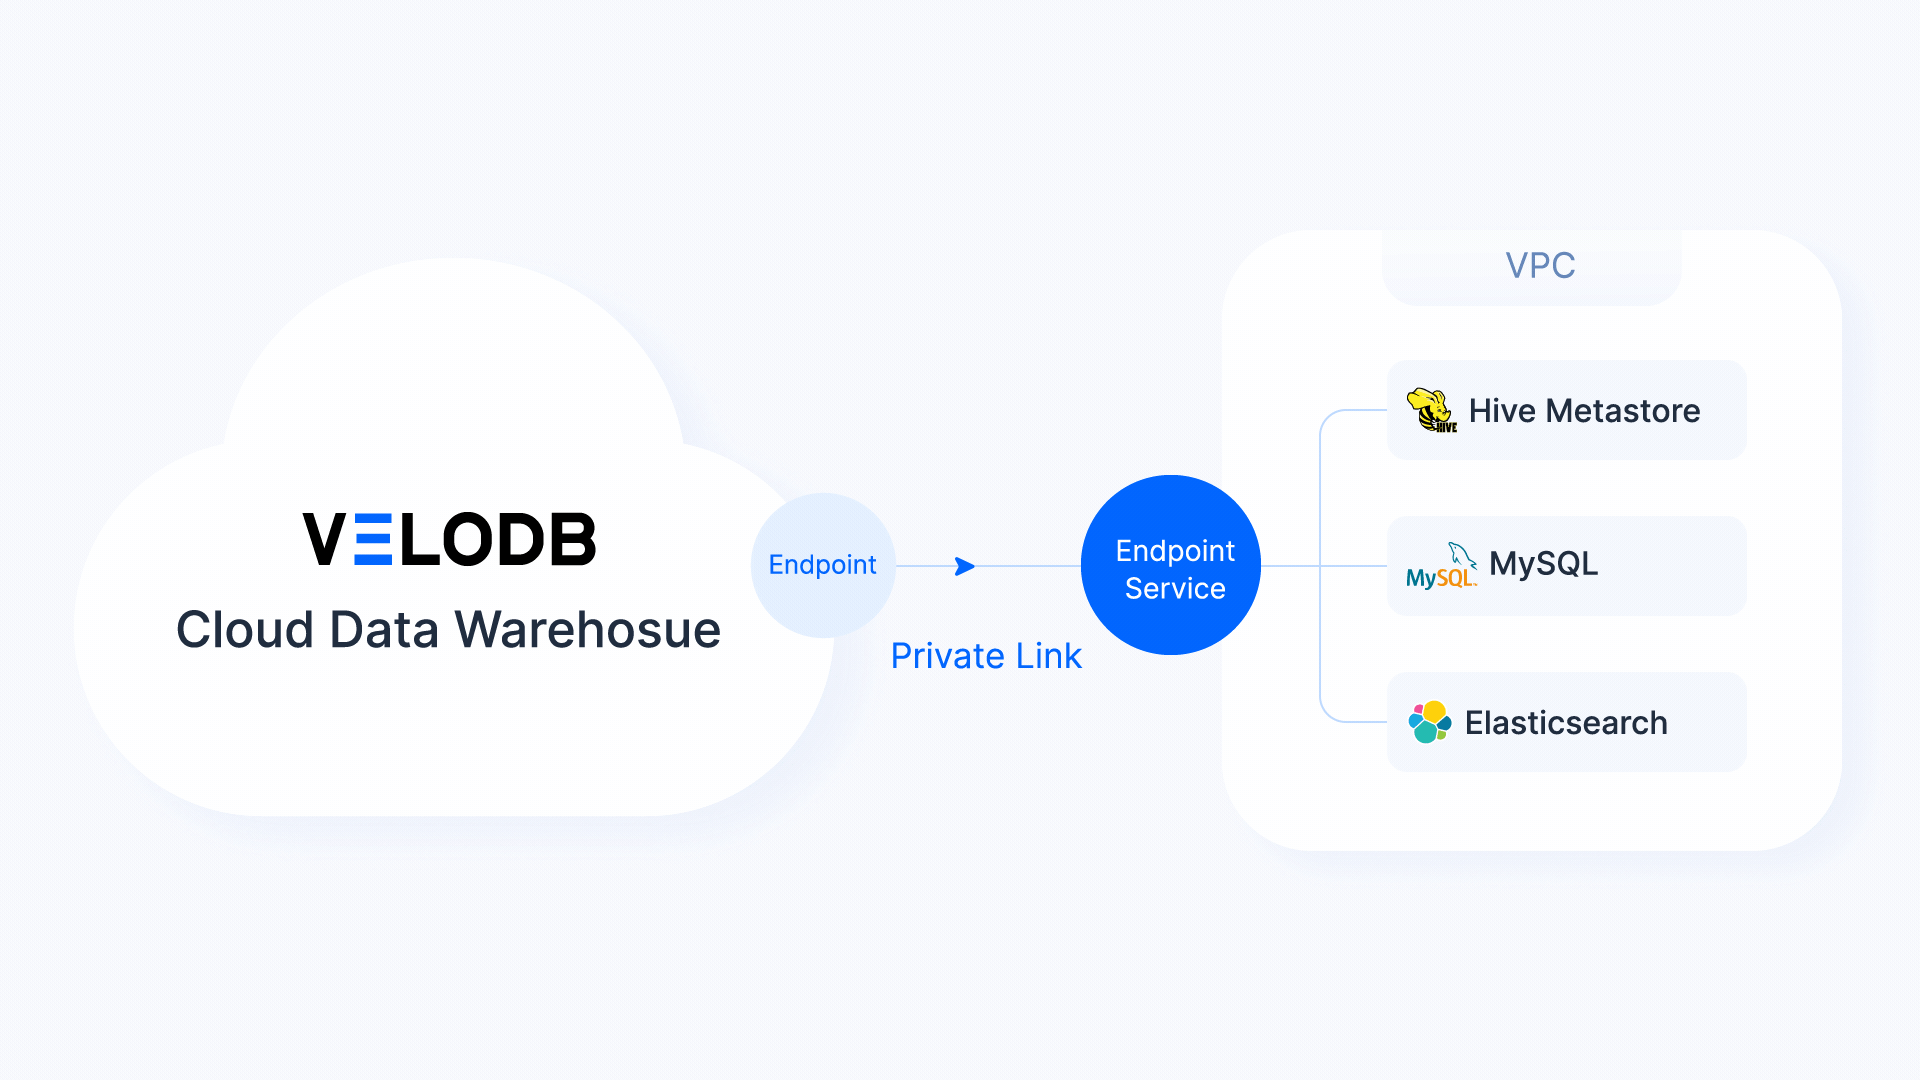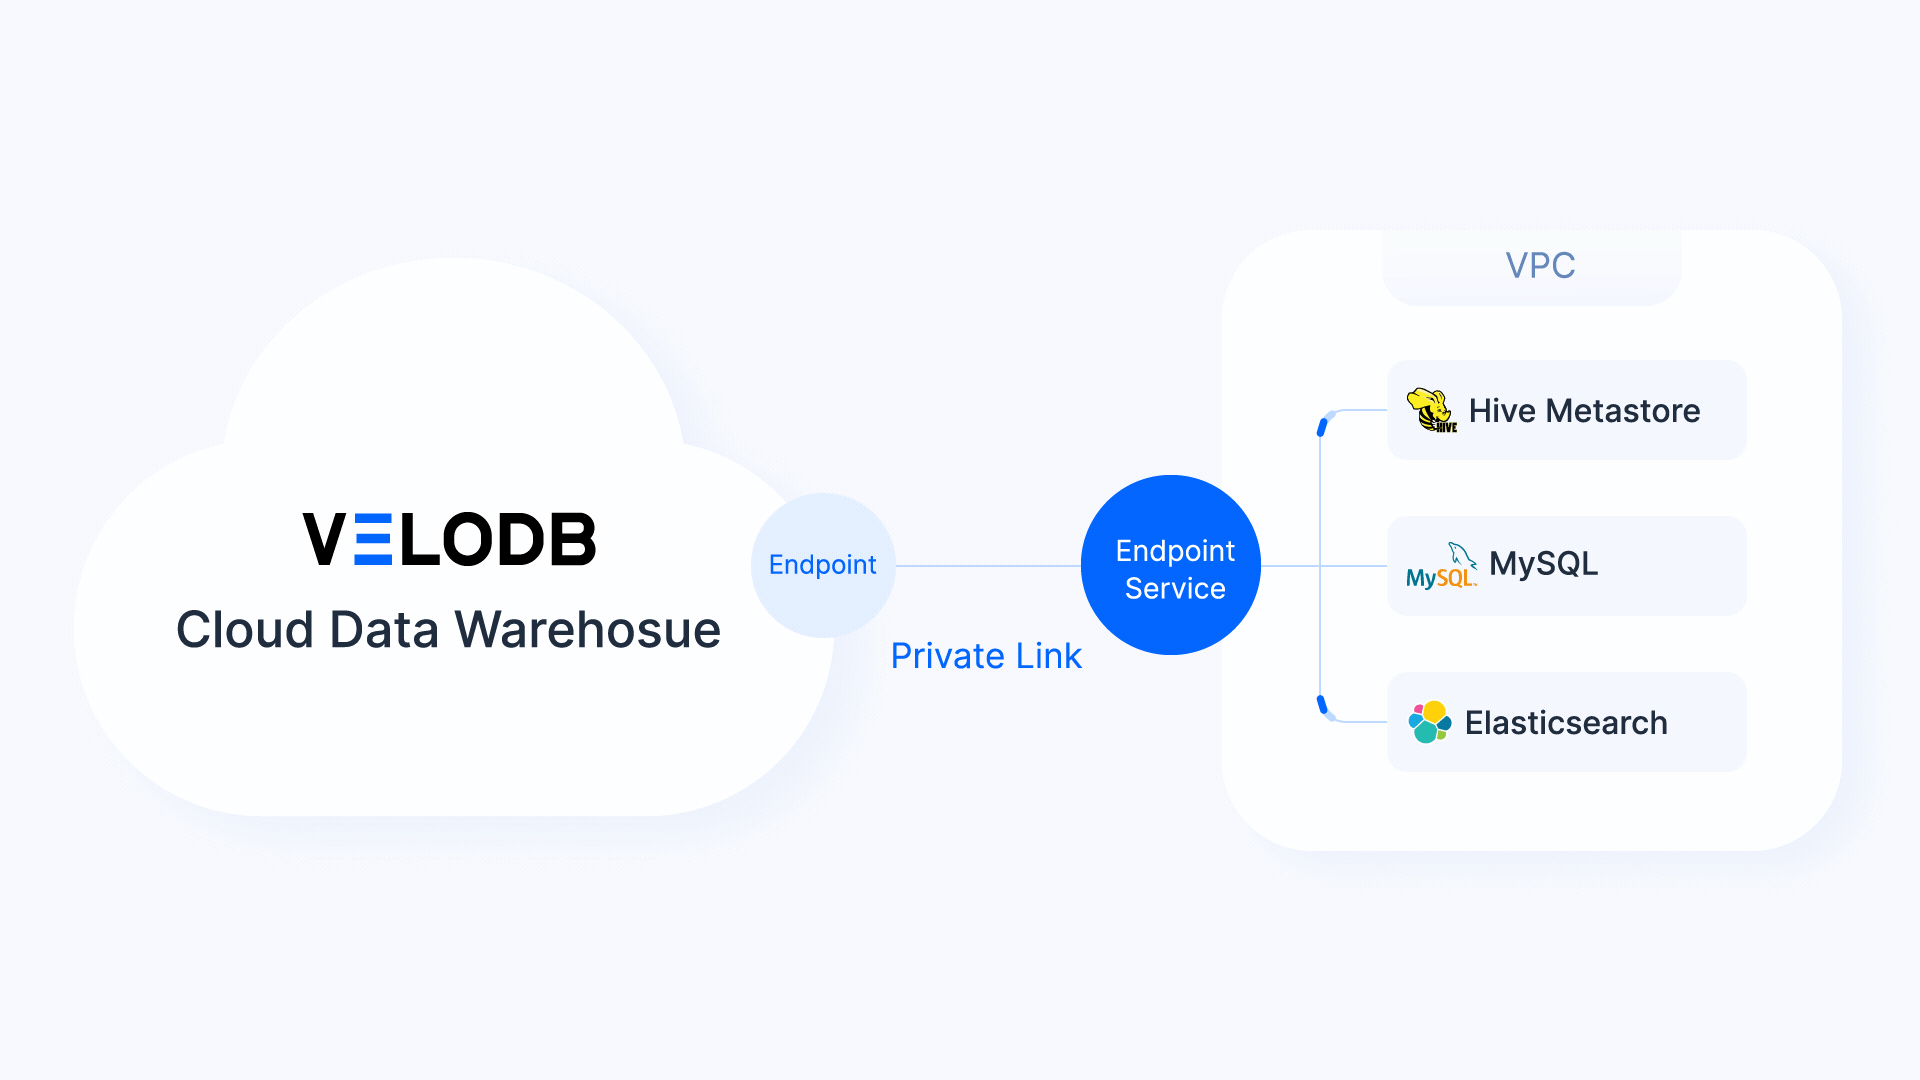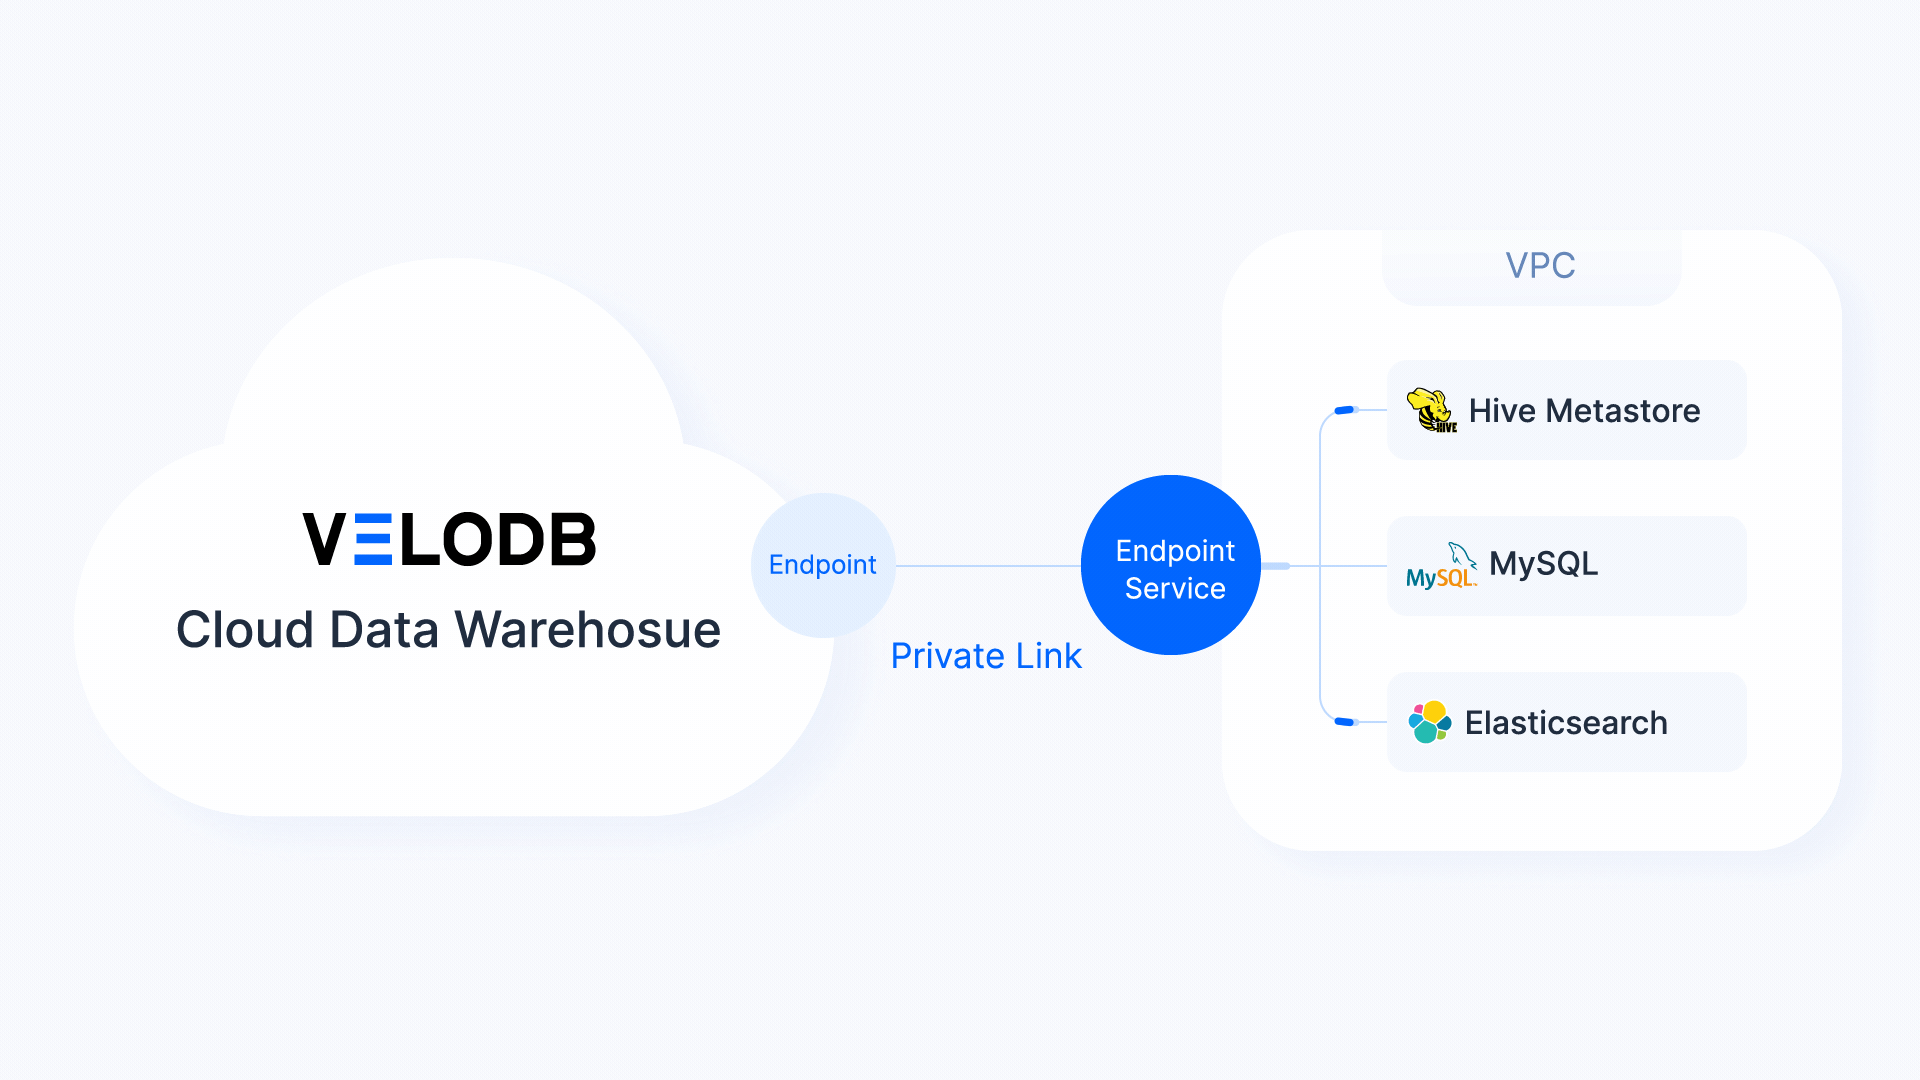
You create and own the Endpoint Service in your VPC or VNet. VeloDB Cloud creates and manages the private Endpoint that connects to your service.
Internet Protocol (IP) allowlists do not apply to private connections. You configure and manage the endpoint service, load balancer, security groups, routing, and data-source network controls in your cloud account. Cloud-provider network charges may apply. Data transferred from your VPC or VNet into the SaaS warehouse is ingress, while data transferred in the other direction is egress. Both may incur the VeloDB Cloud Data Transfer Fee.
Create the endpoint service in the same cloud provider and region as the warehouse. The procedure differs by cloud provider and requires you to provide the service identifier and supporting information to VeloDB Cloud.
Before you begin
- Confirm that the private data source is reachable from the VPC or VNet where you will create the endpoint service.
- Confirm that you can create or manage the load balancer, endpoint service, security rules, routes, and data-source allowlists in your cloud account.
- Confirm that the endpoint service region matches the warehouse region.
- Confirm the data-source port and the network controls that must allow traffic from the load balancer.
Choose a cloud provider
Follow the procedure for your cloud provider:
After VeloDB Cloud creates the private endpoint, return to the Connection page and refresh the connection status. The connection is ready when the status shows Connected.