Google Cloud Preparation
Creating a BYOC warehouse on Google Cloud involves the following Google Cloud-side tasks:
- Prepare a VPC and subnet.
- (Optional) Review the Terraform template and the resources it creates.
Prepare an existing VPC and subnet
Use an existing VPC only when it and its subnet meet the region, availability-zone, and subnet requirements for the BYOC warehouse. If no VPC and subnet meet these requirements, create them in advance.
Note:
If a VPC and subnet already meet the region, availability zone, and subnet requirements and you want to deploy the BYOC warehouse into them, skip the steps below. For the supported regions, see Supported Regions.
Create a VPC and subnet
-
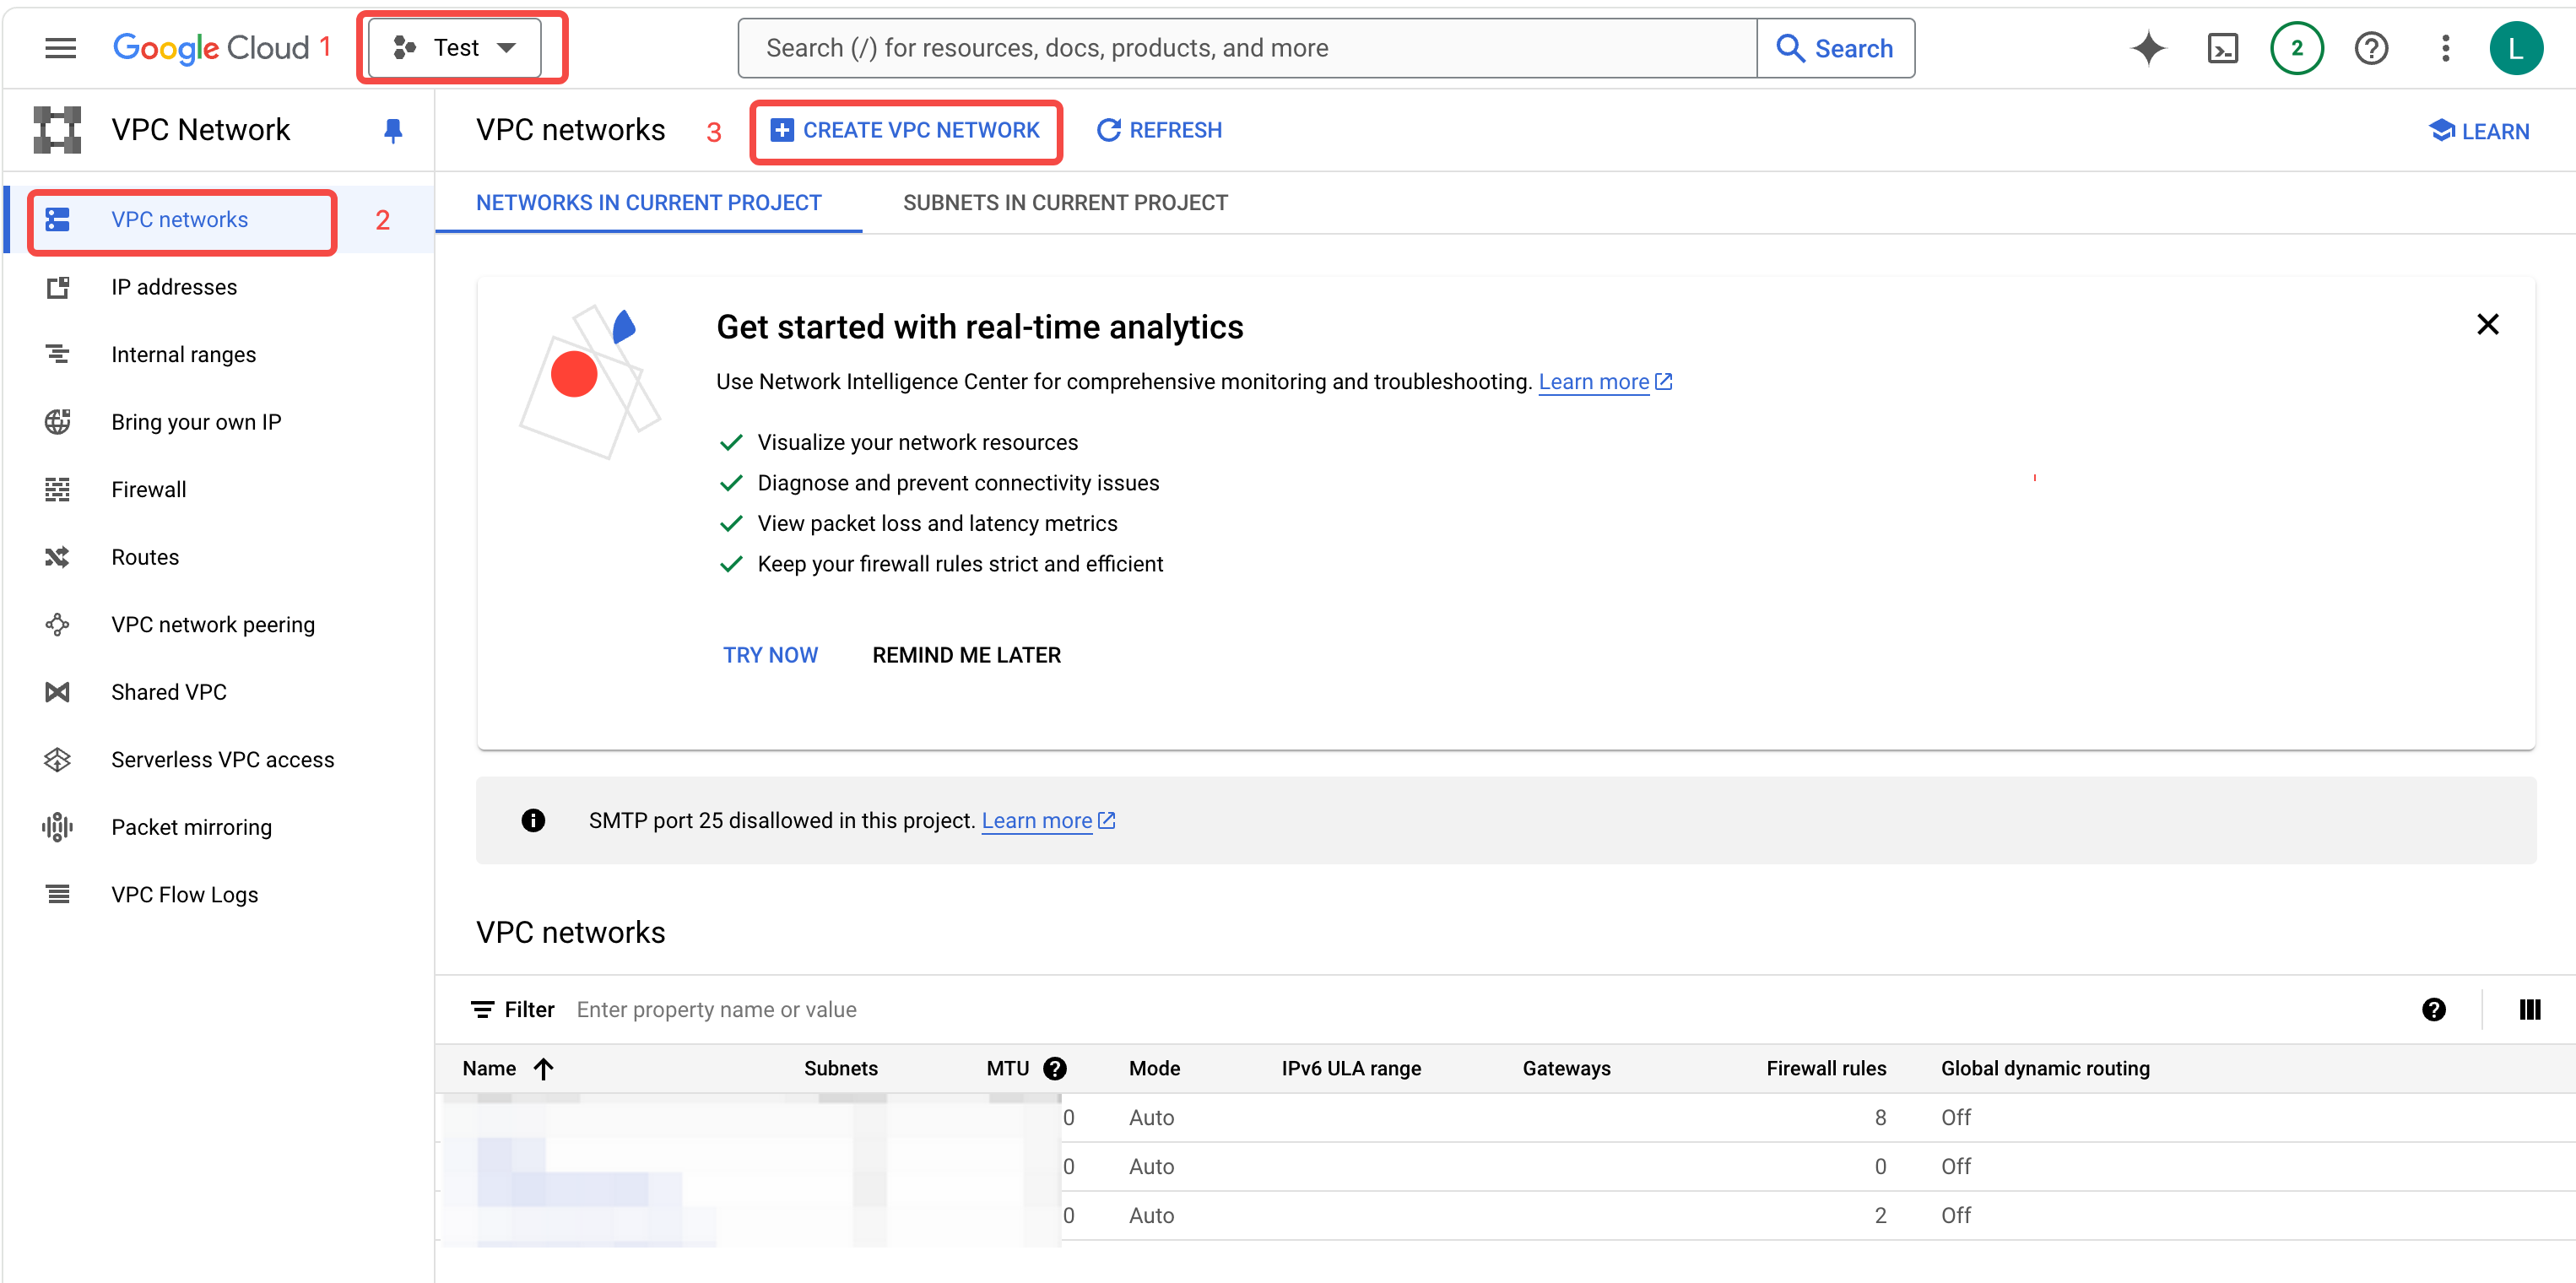
Open the Google Cloud VPC networks console.
-
Click VPC networks > CREATE VPC NETWORK to open the VPC creation page.
-
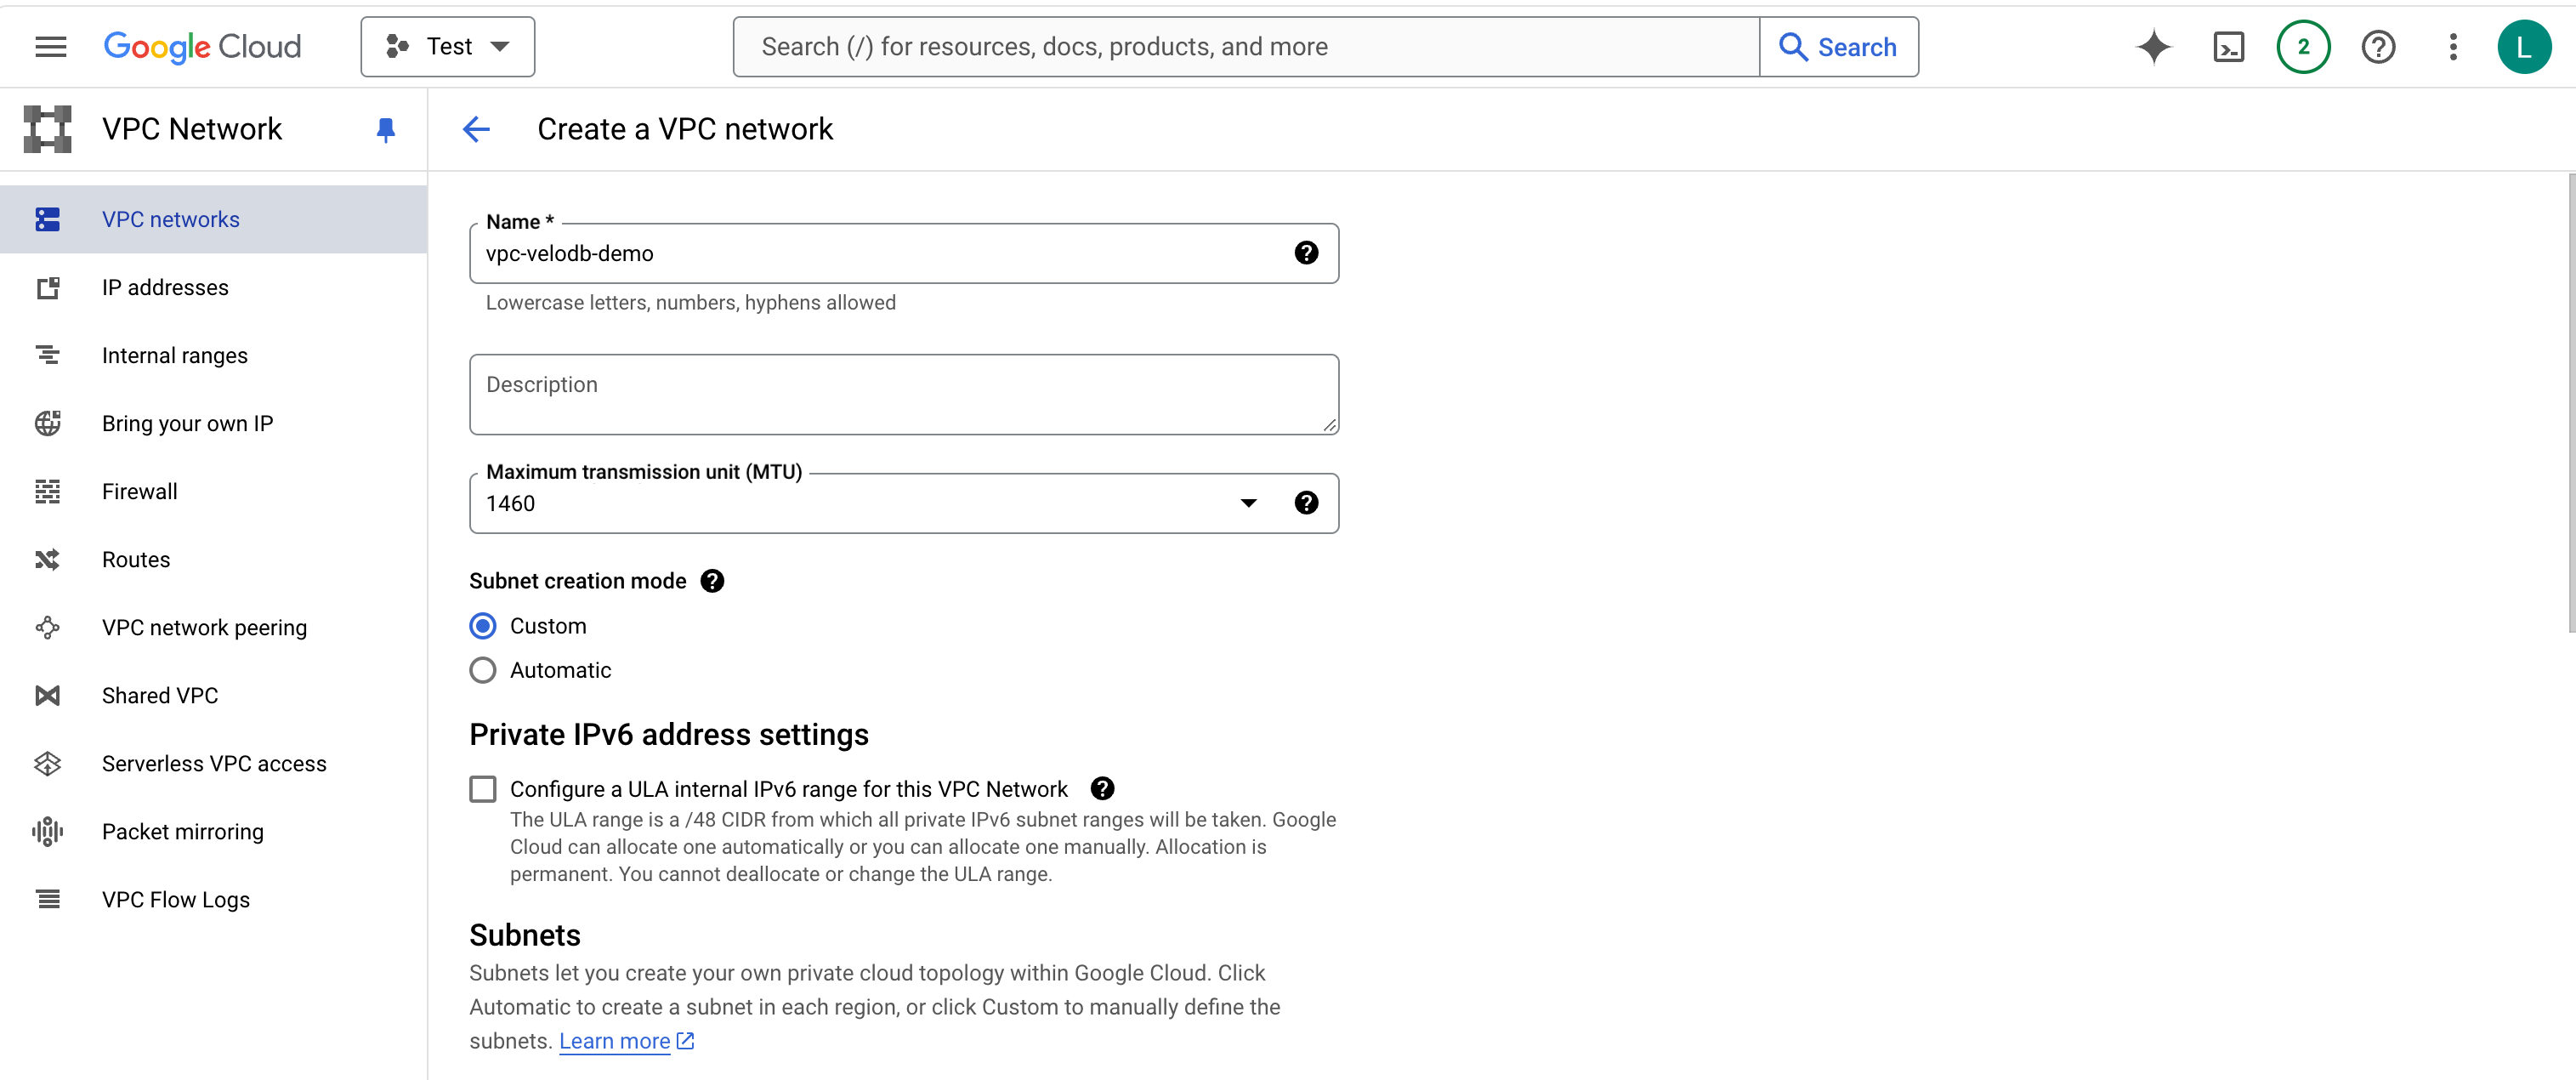
Enter a VPC Name and select Custom mode.
-
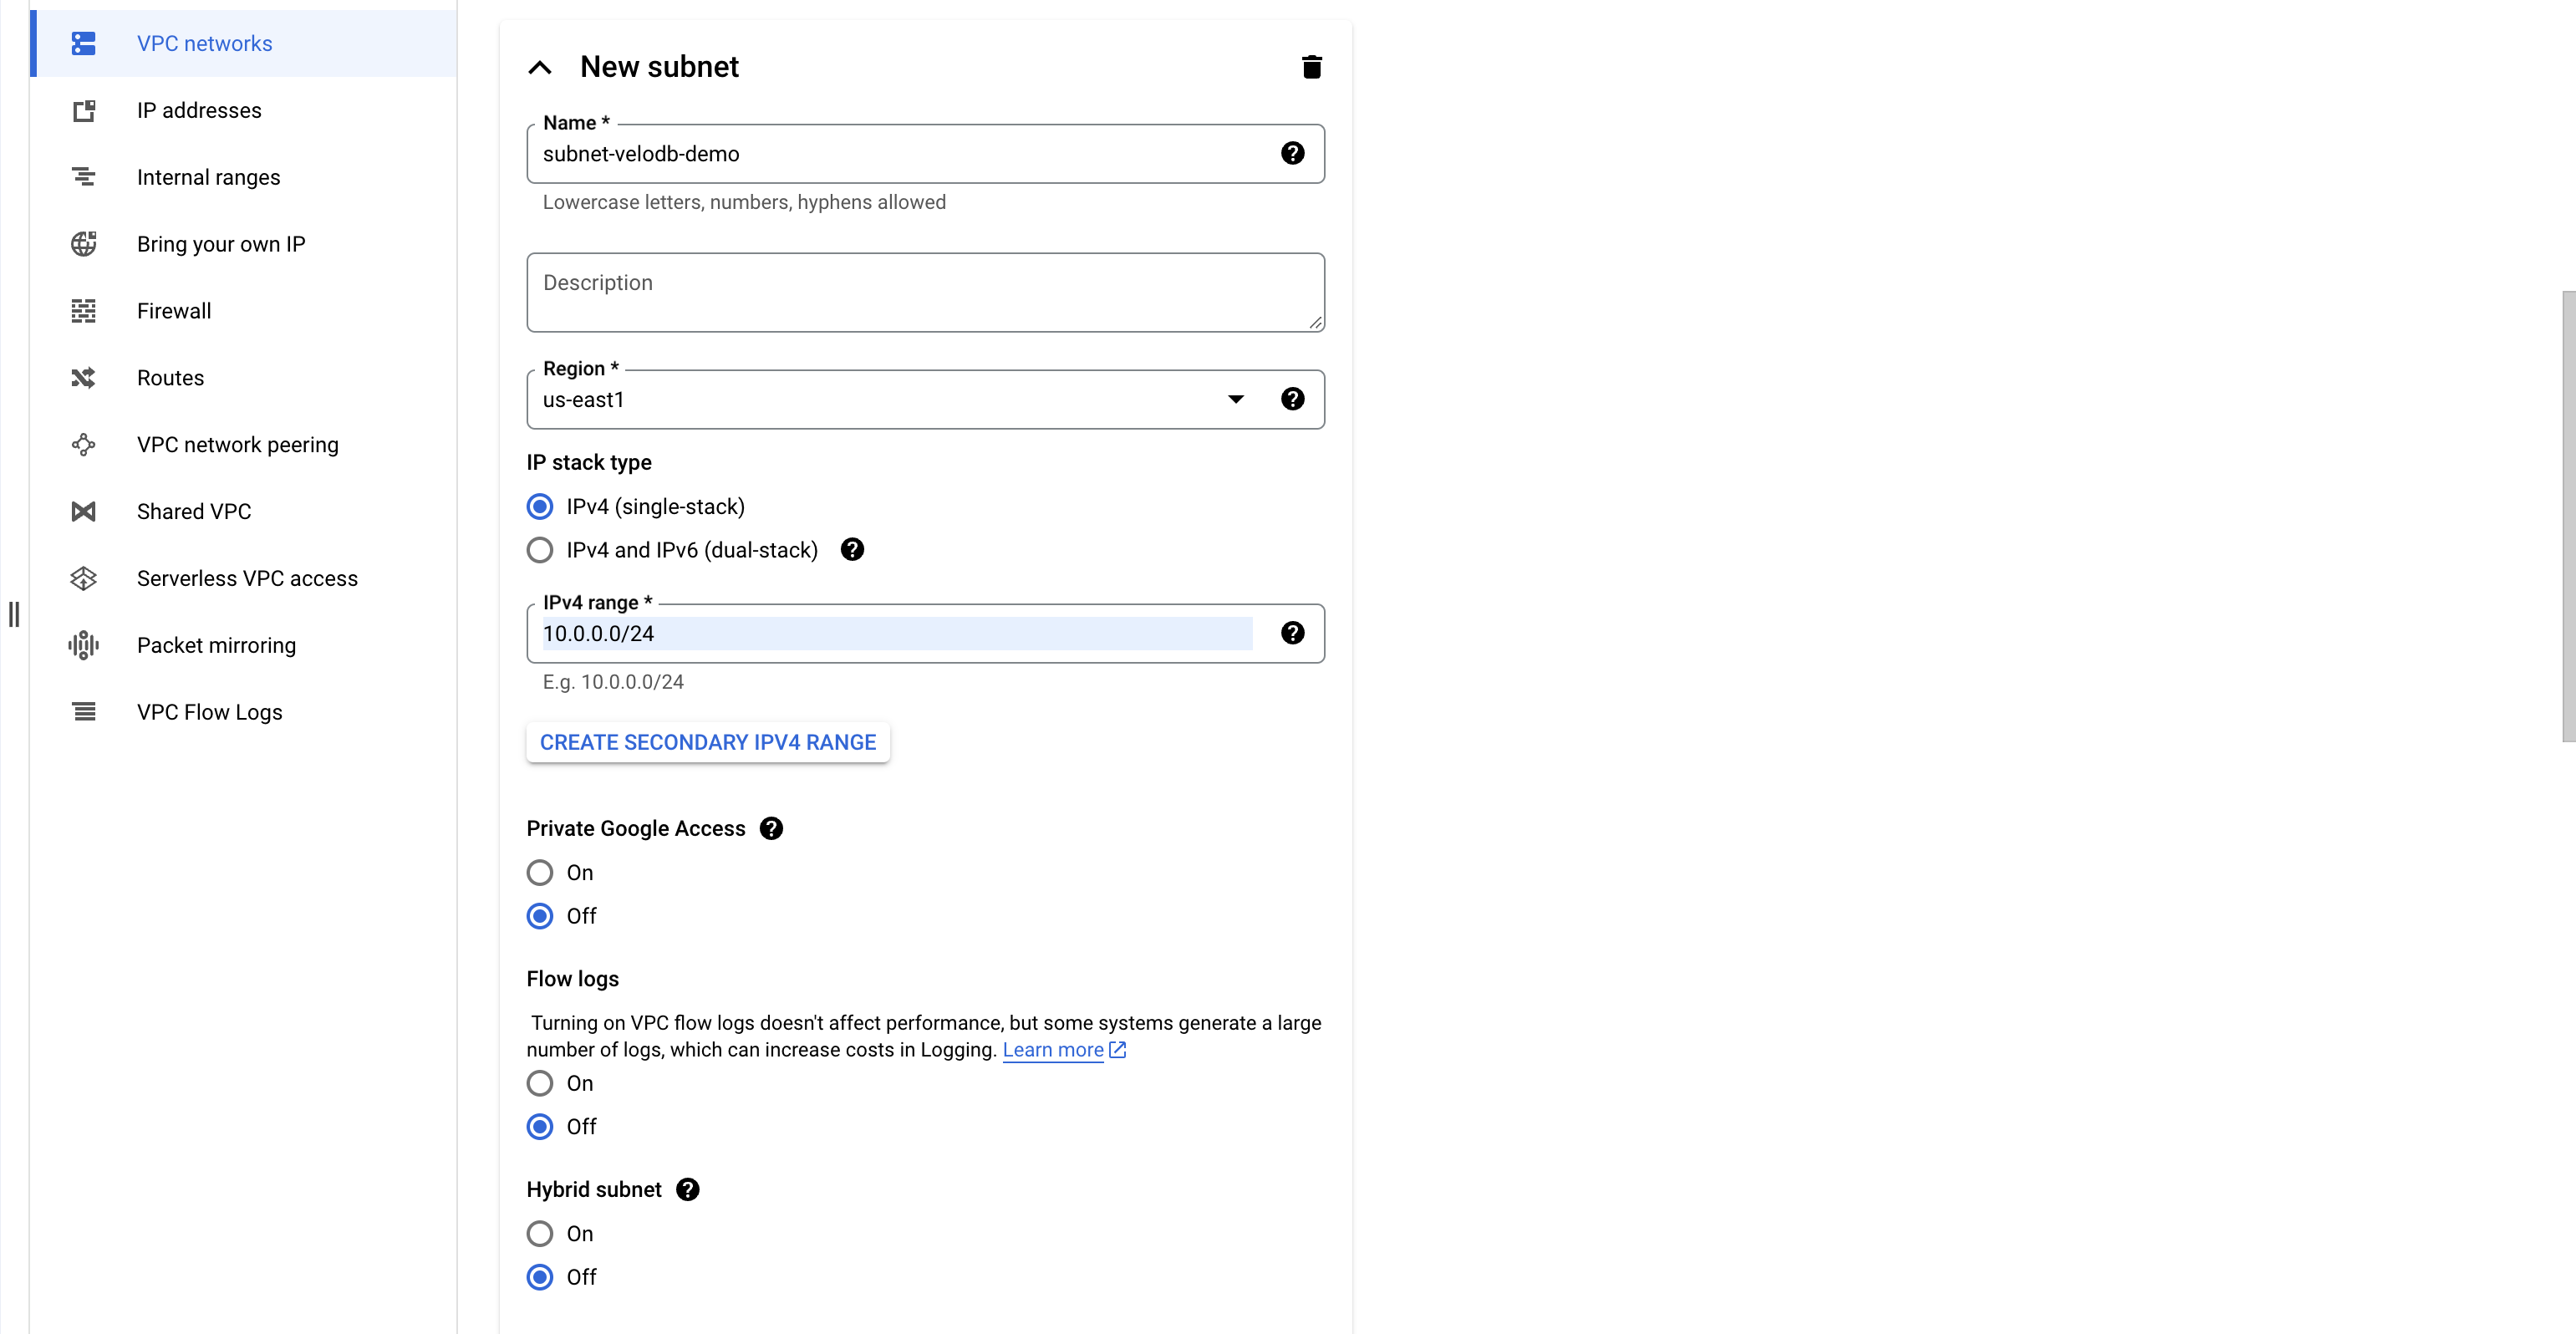
Enter a subnet Name, select a supported Region, and enter an IPv4 range. See Supported Regions.
-
Turn off Private Google Access, Flow logs, and Hybrid subnet.
-
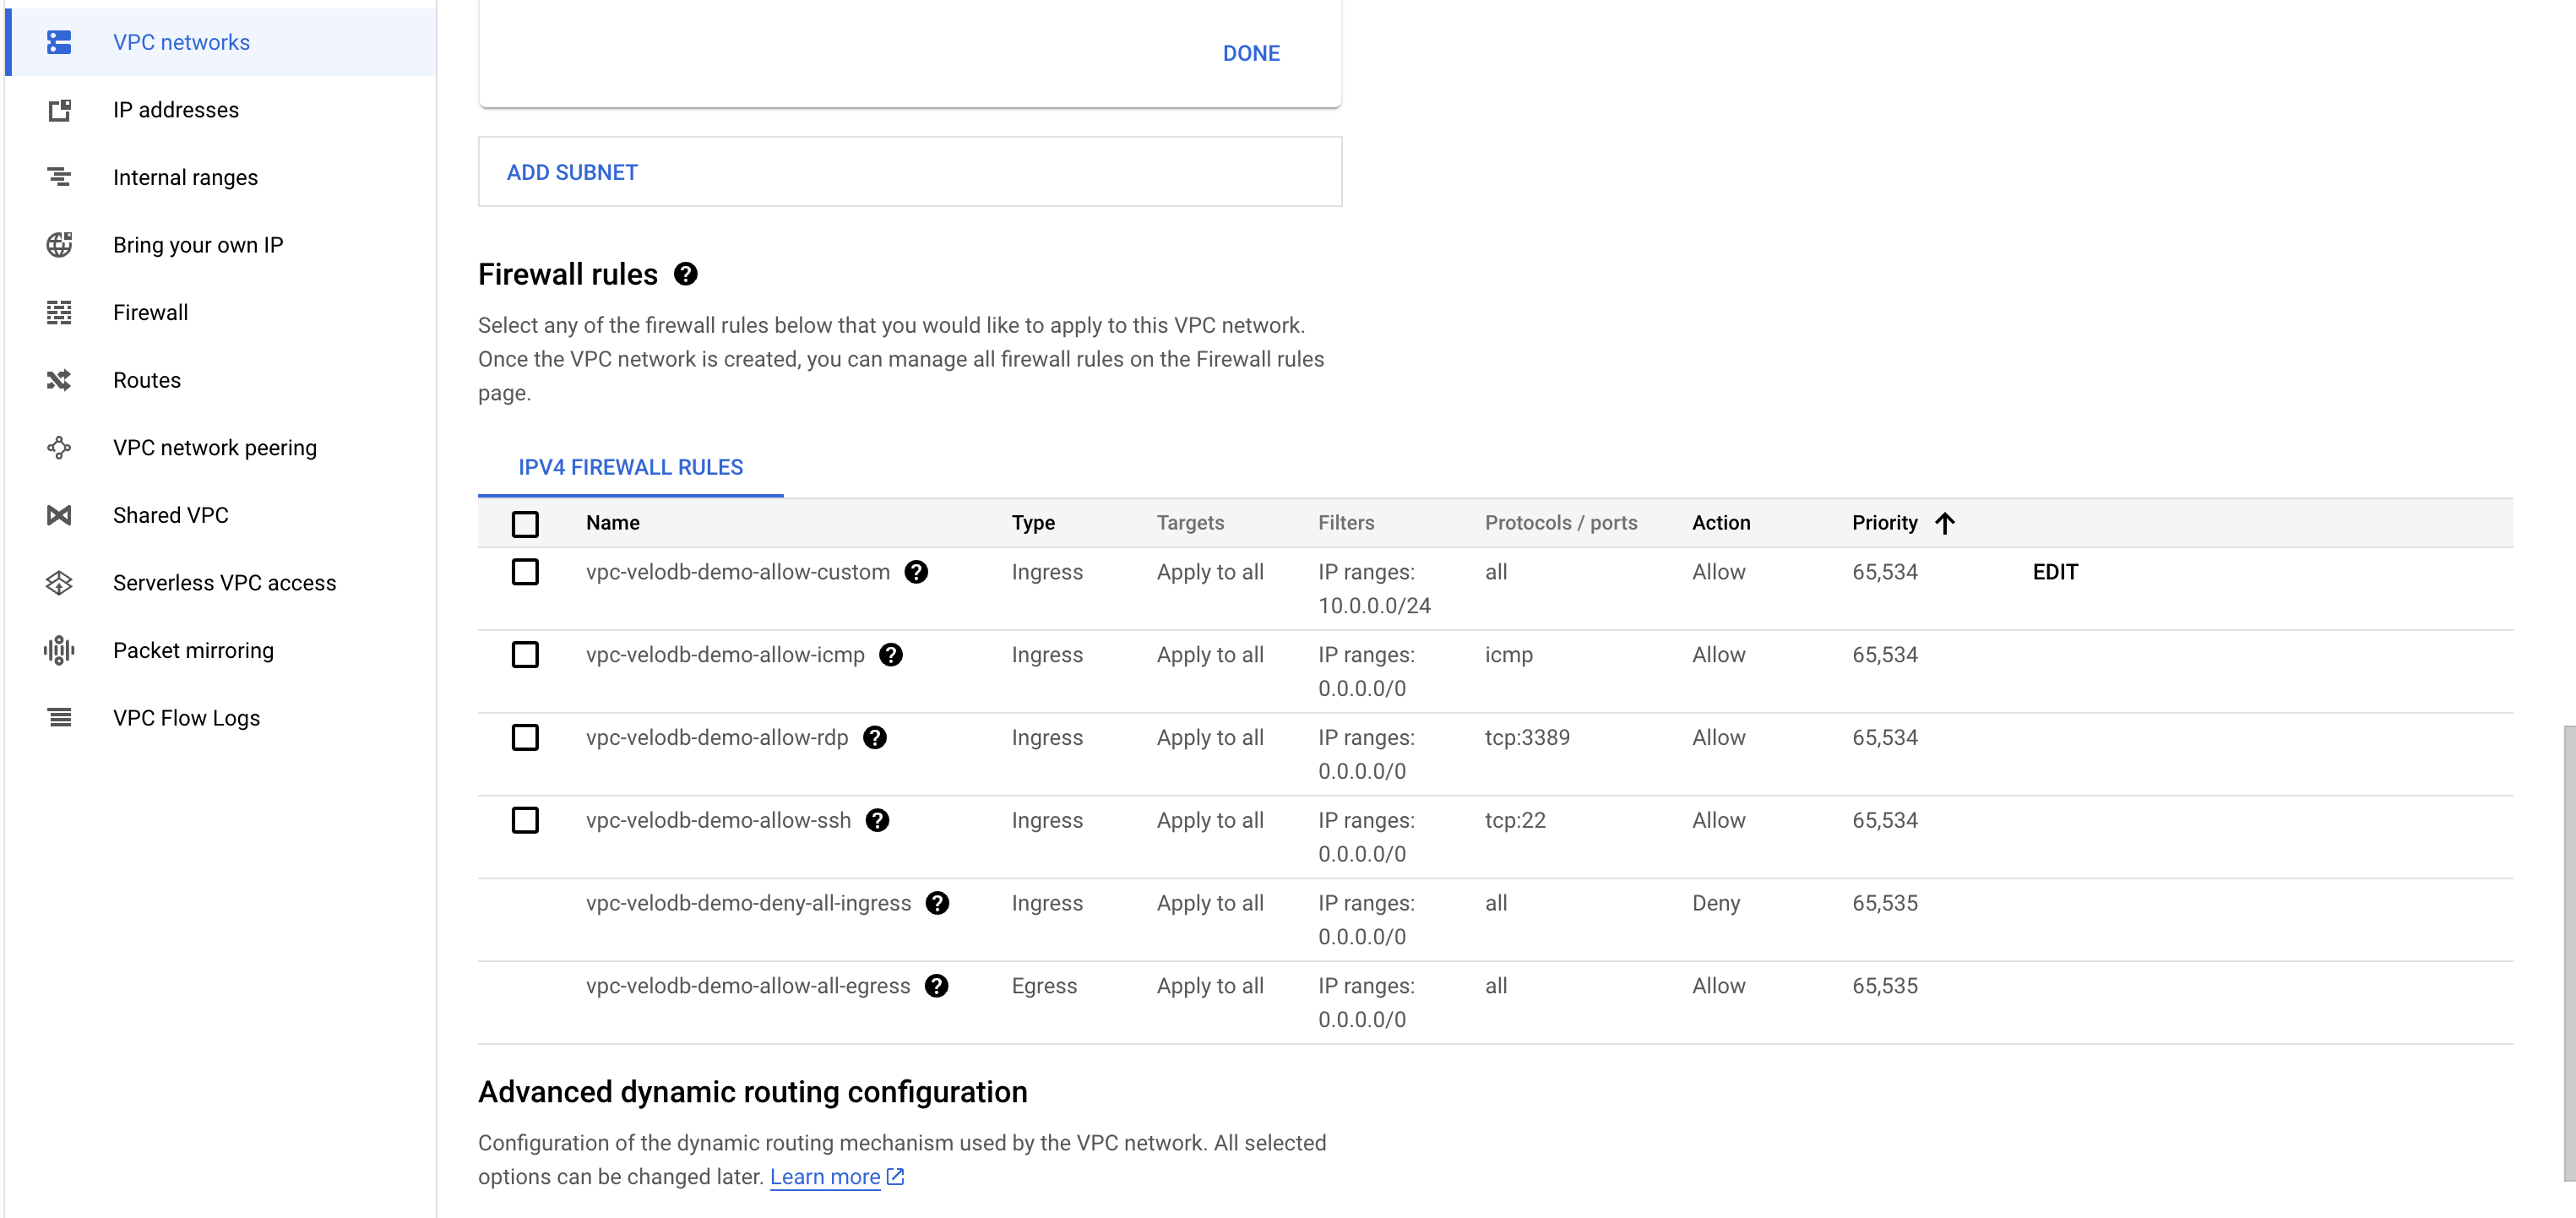
Clear all checkboxes under Firewall rules.
-
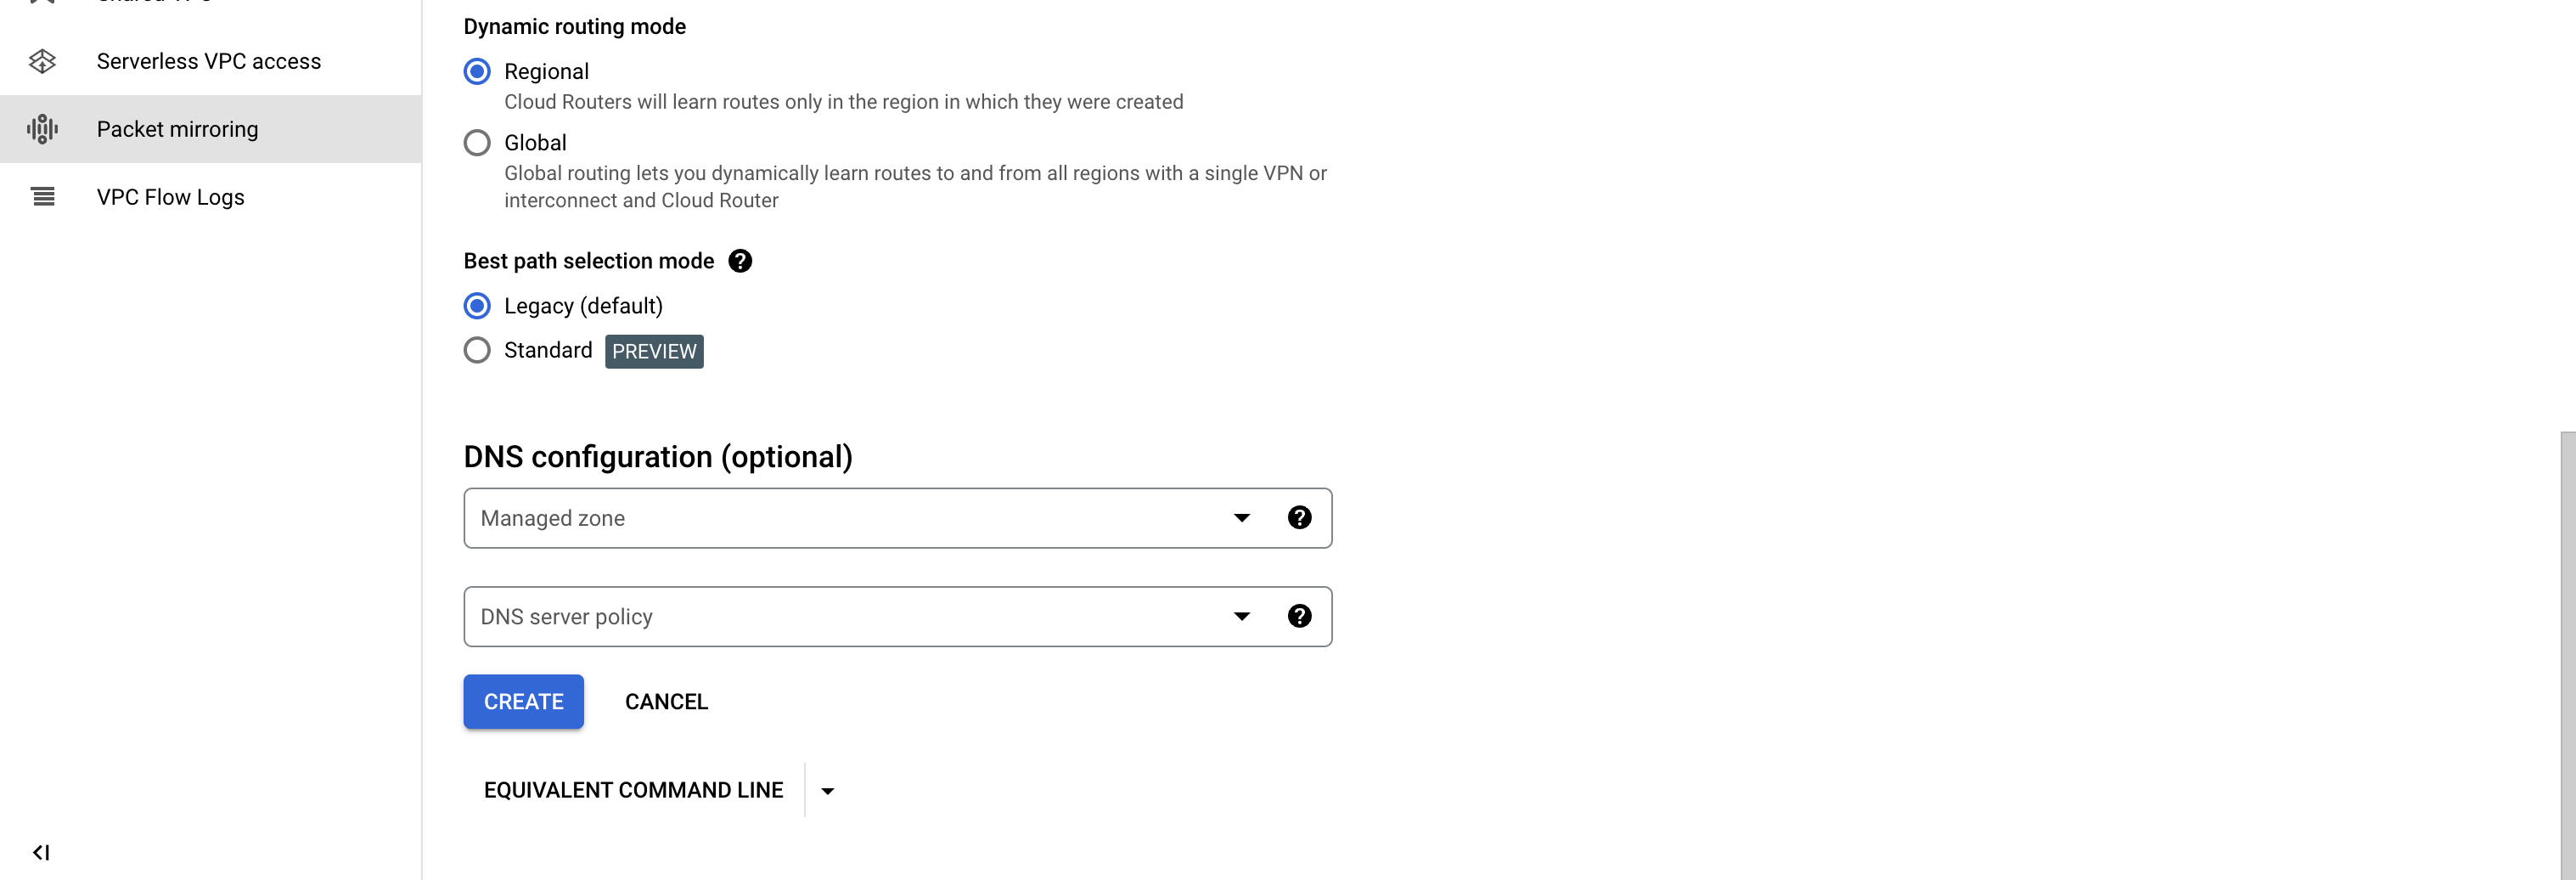
Select Regional for Dynamic routing mode, and Legacy for Best path selection mode.
-
Click CREATE to finish creating the VPC and subnet.
For more information, see the Google Cloud documentation for creating and managing VPC networks.
Review the Terraform template and resources (optional)
Note:
This section is for review only and does not require you to run anything. To run the deployment command that creates a BYOC warehouse, you or the administrator who runs it need the following IAM permissions listed. Template execution fails if these permissions are missing.
The Terraform template runs in your Google Cloud project and creates or manages resources such as VPC components, Compute Engine instances, and Cloud Storage buckets. It requires the IAM permissions listed below.
Review the Terraform template
The VeloDB Cloud Terraform template runs in your Google Cloud project. Review the template before deployment to understand the resources it creates.
When you run the template in Google Cloud Shell, it deploys the Agent. The Agent establishes a private connection to VeloDB Cloud and completes warehouse initialization.
After deployment finishes, open the warehouse in the VeloDB Cloud Console and create a compute cluster for data analysis.
Review the created resources
-
Compute Engine instance
- Name:
VeloDBAgent - Purpose: Runs the Agent, Prometheus, Fluent Bit, and related programs.
- Name:
-
Private Service Connect endpoint
- Name:
VeloDBEndpoint - Purpose: Establishes a private network connection to the VeloDB Cloud management service for control instructions and monitoring and log delivery.
- Name:
-
VPC firewall rules
- Names:
VeloDBSecurityGroupIngress,VeloDBSecurityGroupEgress - Purpose: Control traffic for VM instances created for the BYOC warehouse, including subnet traffic to port
5000and outbound traffic.
- Names:
-
Cloud Storage bucket
- Name:
VeloDBBucket - Purpose: Stores warehouse data.
- Name:
-
IAM service accounts, custom role, and bucket key
- Names:
VeloDBControlPlaneRole(control plane service account)VeloDBControlPlaneRolePolicy(custom role policy)VeloDBBucketKey(bucket key)VeloDBDataAccessRole(data-access service account)
- Purpose: The service account has the permissions required by the Agent. Subsequent control operations use this service account identity.
- Names:
Review service account permissions
After the Terraform template runs for the first time, it creates a service account that manages resources required by the BYOC warehouse. The following is a list of its permissions.
-
Permission summary:
compute.addresses.createcompute.addresses.createInternalcompute.addresses.deletecompute.addresses.deleteInternalcompute.addresses.setLabelscompute.addresses.getcompute.addresses.listcompute.addresses.usecompute.addresses.useInternalcompute.disks.createcompute.disks.createTagBindingcompute.disks.deletecompute.disks.deleteTagBindingcompute.disks.getcompute.disks.listcompute.disks.resizecompute.disks.setLabelscompute.disks.usecompute.firewalls.createcompute.firewalls.createTagBindingcompute.firewalls.deletecompute.firewalls.deleteTagBindingcompute.firewalls.getcompute.firewalls.listcompute.firewalls.updatecompute.forwardingRules.createcompute.forwardingRules.deletecompute.forwardingRules.getcompute.forwardingRules.setLabelscompute.instanceGroups.createcompute.instanceGroups.deletecompute.instanceGroups.updatecompute.instanceGroups.usecompute.instances.attachDiskcompute.instances.createcompute.instances.createTagBindingcompute.instances.deletecompute.instances.deleteTagBindingcompute.instances.detachDiskcompute.instances.getcompute.instances.getEffectiveFirewallscompute.instances.listcompute.instances.listTagBindingscompute.instances.osAdminLogincompute.instances.osLogincompute.instances.resetcompute.instances.resumecompute.instances.setDiskAutoDeletecompute.instances.setLabelscompute.instances.setMachineTypecompute.instances.setMetadatacompute.instances.setNamecompute.instances.setServiceAccountcompute.instances.setTagscompute.instances.startcompute.instances.stopcompute.instances.suspendcompute.instances.updatecompute.instances.usecompute.networks.getcompute.networks.listcompute.networks.updatePolicycompute.networks.usecompute.regionBackendServices.createcompute.regionBackendServices.createTagBindingcompute.regionBackendServices.deletecompute.regionBackendServices.deleteTagBindingcompute.regionBackendServices.getcompute.regionBackendServices.getIamPolicycompute.regionBackendServices.listcompute.regionBackendServices.updatecompute.regionBackendServices.usecompute.regionHealthChecks.createcompute.regionHealthChecks.deletecompute.regionHealthChecks.useReadOnlycompute.subnetworks.getcompute.subnetworks.listcompute.subnetworks.usecompute.zoneOperations.get
The following sections group the permissions by resource type.
-
Compute Engine permissions:
-
Manage VM instances.
compute.disks.createcompute.disks.createTagBindingcompute.disks.deletecompute.disks.deleteTagBindingcompute.disks.getcompute.disks.listcompute.disks.resizecompute.disks.setLabelscompute.disks.usecompute.instanceGroups.createcompute.instanceGroups.deletecompute.instanceGroups.updatecompute.instanceGroups.usecompute.instances.attachDiskcompute.instances.createcompute.instances.createTagBindingcompute.instances.deletecompute.instances.deleteTagBindingcompute.instances.detachDiskcompute.instances.getcompute.instances.getEffectiveFirewallscompute.instances.listcompute.instances.listTagBindingscompute.instances.osAdminLogincompute.instances.osLogincompute.instances.resetcompute.instances.resumecompute.instances.setDiskAutoDeletecompute.instances.setLabelscompute.instances.setMachineTypecompute.instances.setMetadatacompute.instances.setNamecompute.instances.setServiceAccountcompute.instances.setTagscompute.instances.startcompute.instances.stopcompute.instances.suspendcompute.instances.updatecompute.instances.use -
Manage firewall rules.
compute.firewalls.createcompute.firewalls.createTagBindingcompute.firewalls.deletecompute.firewalls.deleteTagBindingcompute.firewalls.getcompute.firewalls.listcompute.firewalls.update
-
-
VPC Network permissions:
-
Get VPC-related resource information.
compute.networks.getcompute.networks.listcompute.networks.updatePolicycompute.networks.usecompute.subnetworks.getcompute.subnetworks.listcompute.subnetworks.usecompute.zoneOperations.get -
Manage load-balancer resources.
compute.addresses.createcompute.addresses.createInternalcompute.addresses.deletecompute.addresses.deleteInternalcompute.addresses.setLabelscompute.addresses.getcompute.addresses.listcompute.addresses.usecompute.addresses.useInternalcompute.forwardingRules.createcompute.forwardingRules.deletecompute.forwardingRules.getcompute.forwardingRules.setLabelscompute.regionBackendServices.createcompute.regionBackendServices.createTagBindingcompute.regionBackendServices.deletecompute.regionBackendServices.deleteTagBindingcompute.regionBackendServices.getcompute.regionBackendServices.getIamPolicycompute.regionBackendServices.listcompute.regionBackendServices.updatecompute.regionBackendServices.usecompute.regionHealthChecks.createcompute.regionHealthChecks.deletecompute.regionHealthChecks.useReadOnly
-
-
Cloud Storage permissions:
-
Manage specific buckets and read and write their contents.
roles/storage.admin
-
-
Account permissions:
-
Allow the newly created service account to be associated with VM instances so that they can perform operations as that service account.
roles/iam.serviceAccountUser
-
See also
- Create a BYOC Warehouse on Google Cloud: create a BYOC warehouse with a new or existing VPC.
- Supported Regions: select a supported Google Cloud region.